AWS Service Deliveries
AWS Config Services for Continuous Compliance and Configuration Management
GoCloud’s AWS Config delivery builds reliable configuration-management frameworks that give you continuous visibility and control across multi-account environments, so compliance is something you can prove, not just hope for.
Benefits
Continuous control over every configuration
AWS Config turns resource sprawl into an always-current, audit-ready record you can act on.
Continuous Configuration Monitoring
Config records every configuration change across supported resources, timestamped and mapped to resource relationships, giving you a current audit trail.
Automated Compliance Assessment
Config Rules evaluate resources against your policies automatically, flagging non-compliant resources the moment they drift, with the detail your team needs to remediate fast.
Detailed Configuration History
A full history captures the state of every resource at each point in time, with the context needed to investigate, troubleshoot, and audit with confidence.
Resource Relationship Mapping
Config automatically discovers how resources relate, so a change in one place is tracked alongside its impact on everything connected to it.
Features of AWS Config Services
Configuration Recording
Config records details for critical resources including EC2, VPC components, IAM roles, S3 buckets, and RDS databases, building a complete historical record of change.
AWS Config Rules
Define the configurations you require and evaluate reality against them, using AWS managed rules or custom rules built for your governance needs.
Snapshots & History
Point-in-time snapshots capture the state of all recorded resources, so you can track change, troubleshoot issues, and pass compliance audits across the full resource lifecycle.
AWS Config Services Expertise at GoCloud
GoCloud turns framework requirements into enforced, monitored controls, then automates the response when something drifts.
Compliance Configuration Management
We design Config implementations aligned to CIS, PCI DSS, HIPAA, and SOC 2, translating each requirement into controls you can monitor and prove.
Centralized Multi-Account Visibility
We deploy Config aggregators across AWS Organizations to deliver a single, unified view of compliance across every account and region.
Automated & Governed Remediation
We integrate Config with Systems Manager, Lambda, and SNS to detect drift and remediate it automatically, within the guardrails you define.
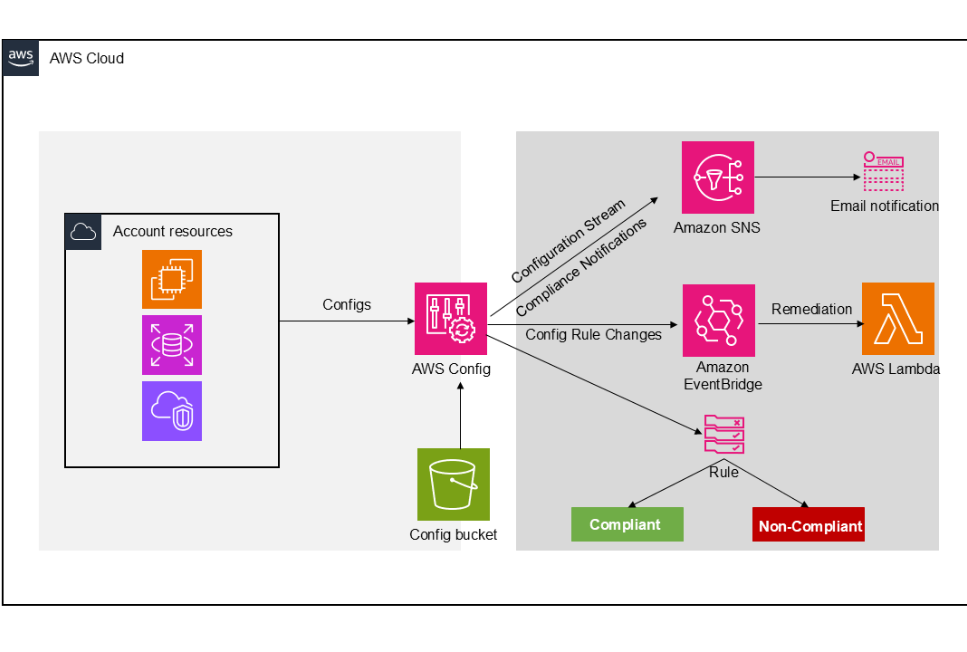
AWS Config Multi-Account Architecture
Config recorders in every account feed a central aggregator that evaluates rules, triggers remediation, and preserves a durable history.
Client Success Stories
Enterprise-grade solutions designed to modernize infrastructure, accelerate delivery, and improve operational efficiency on AWS.
Zero-Downtime Blue/Green Migration on a Hardened Private Architecture
Moving Morado's Threatnote threat intelligence platform off Elastic Beanstalk into a containerized, privately networked ECS Fargate environment.
Read More
Scaling a Telehealth Platform Without Slowing Down Audits
Scaling telehealth on Amazon EKS and RDS, with monitoring and access controls wired into every deployment.
Read MoreAWS Control Tower for Secure, Scalable Governance
Moving a single-account AI platform into a governed multi-account Landing Zone with isolated environments and preventive guardrails.
Read MoreA Cross-Border Payment Platform Built to Be Audited
Making every cross-border transfer traceable through ECS, Control Tower account boundaries and centralised logging.
Read MoreStreaming Telemetry and AI-Assisted Operations at Zito Networks
A containerized observability platform bringing together streaming gNMI telemetry and multi-protocol device monitoring.
Read More
Building a Secure, Scalable Restaurant Platform on AWS
Transforming Plattir's server-based infrastructure into a secure, scalable, containerized architecture on Amazon Web Services.
Read More
Production Agentic Platform Migrated to AWS
Building the complete AWS platform from scratch and migrating three production environments with continuous data replication.
Read More
Zero-Downtime Blue/Green Migration on a Hardened Private Architecture
Moving Morado's Threatnote threat intelligence platform off Elastic Beanstalk into a containerized, privately networked ECS Fargate environment.
Read More
Scaling a Telehealth Platform Without Slowing Down Audits
Scaling telehealth on Amazon EKS and RDS, with monitoring and access controls wired into every deployment.
Read MoreAWS Control Tower for Secure, Scalable Governance
Moving a single-account AI platform into a governed multi-account Landing Zone with isolated environments and preventive guardrails.
Read MoreA Cross-Border Payment Platform Built to Be Audited
Making every cross-border transfer traceable through ECS, Control Tower account boundaries and centralised logging.
Read MoreStreaming Telemetry and AI-Assisted Operations at Zito Networks
A containerized observability platform bringing together streaming gNMI telemetry and multi-protocol device monitoring.
Read More
Building a Secure, Scalable Restaurant Platform on AWS
Transforming Plattir's server-based infrastructure into a secure, scalable, containerized architecture on Amazon Web Services.
Read More
Production Agentic Platform Migrated to AWS
Building the complete AWS platform from scratch and migrating three production environments with continuous data replication.
Read More
Start your AWS transformation journey with GoCloud
Let’s design your AWS roadmap and build a secure, scalable cloud foundation tailored to your business needs.