

Our Product
MobSecAI Secure Every Mobile App Before Attackers Do
Overview
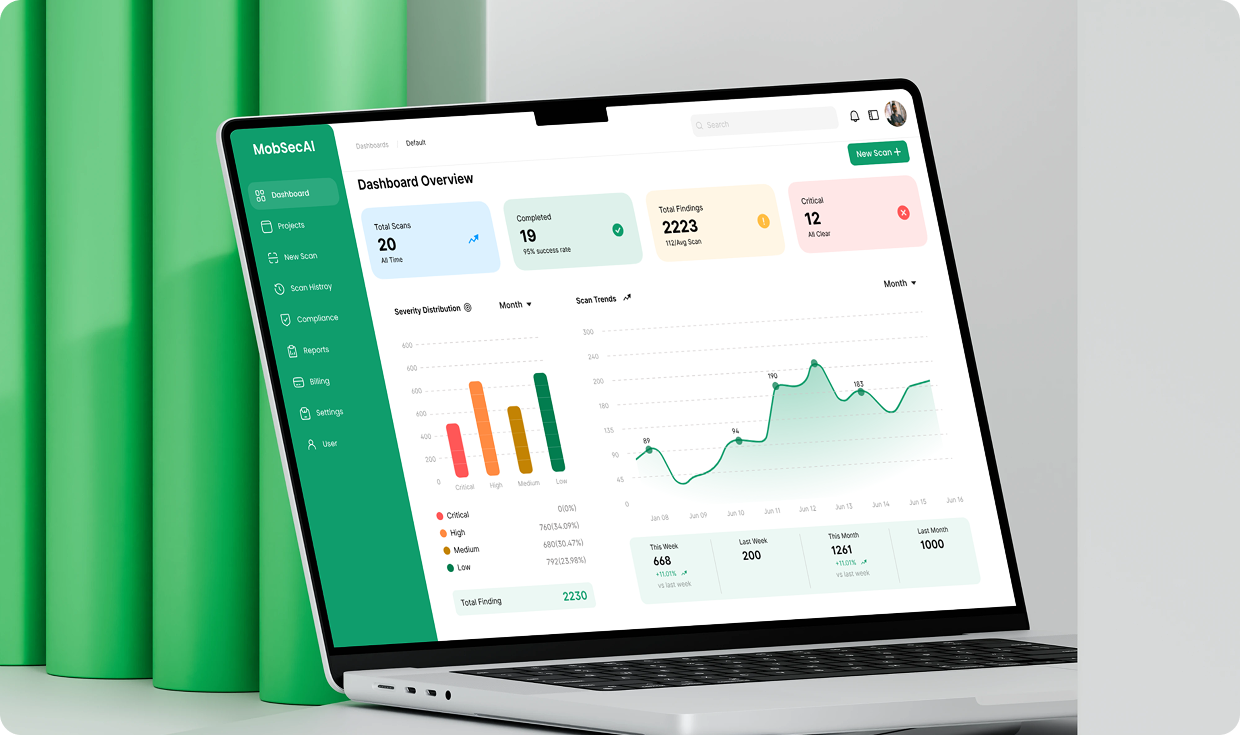
Five layers of defense in one platform
Static Analysis (SAST)
Deep code inspection across APK, IPA, XAPK and AAB builds hardcoded secrets, API keys and tokens, insecure cryptography, debug flags left enabled, and unsafe data storage found without running the app.
Dynamic Analysis (DAST)
Runtime instrumentation in sandboxed emulators: SSL pinning bypasses, file access at runtime, insecure network traffic, and behaviour the code alone never reveals.
Malware & Threat Detection
Threat intelligence for accessibility-service abuse, SMS fraud, clipboard hijacking, keylogging and hidden crypto mining including behaviour inherited from third-party SDKs you didn't write.
Privacy & Permission Analysis
PII collection, hidden tracking SDKs and excessive permission requests, each mapped to the regulation it affects so a privacy finding arrives with its GDPR or HIPAA context already attached.
API Testing
The endpoints behind the app: broken authentication and object-level authorization, over-permissive responses, missing rate limits and unencrypted transport.
From an uploaded build to a ranked findings list automatically
Any build format, any stage
Pre-release candidates, production builds or a competitor's public listing.
No source required
Testing runs against the compiled artifact, the same thing an attacker downloads.
Results while you wait
Static findings surface first; dynamic and API results follow as the run completes.
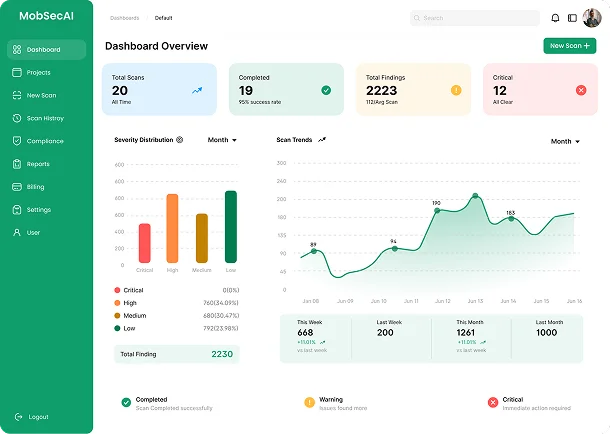
From a finding to a fix your team can ship
Ranked by real risk
Exploitability and data exposure decide priority, so the list reflects what to fix first.
Evidence attached
Traffic captures, decompiled snippets and runtime traces support each finding.
Regression tracking
Compare against the previous scan to confirm fixes landed and catch anything reintroduced.

Frequently Asked Questions
What does MobSecAI test for?
How do we submit an app for testing?
Two ways: upload the build directly — APK, IPA, XAPK or APKS — or paste a link to the app instead.
What does the static analysis find?
Deep code inspection across APK, IPA, XAPK and APKS builds, surfacing hardcoded secrets, API keys and insecure crypto.
What does the dynamic analysis add?
Runtime instrumentation in sandboxed emulators, which captures SSL and pinning bypasses, file access and network traffic — behaviour that only appears when the app is actually running.
Can it detect malware and privacy issues?
Yes. A threat intelligence engine flags accessibility-service abuse, SMS fraud, clipboard hijacking, keylogging and crypto mining, while API testing catches PII collection, hidden tracking SDKs and excessive permission requests with regulatory mapping.
What reports do we get at the end?
A detailed report as a password-protected PDF, a summary report as an XLSX, a network traffic report, and access to your previous scan — the last three with no password required.